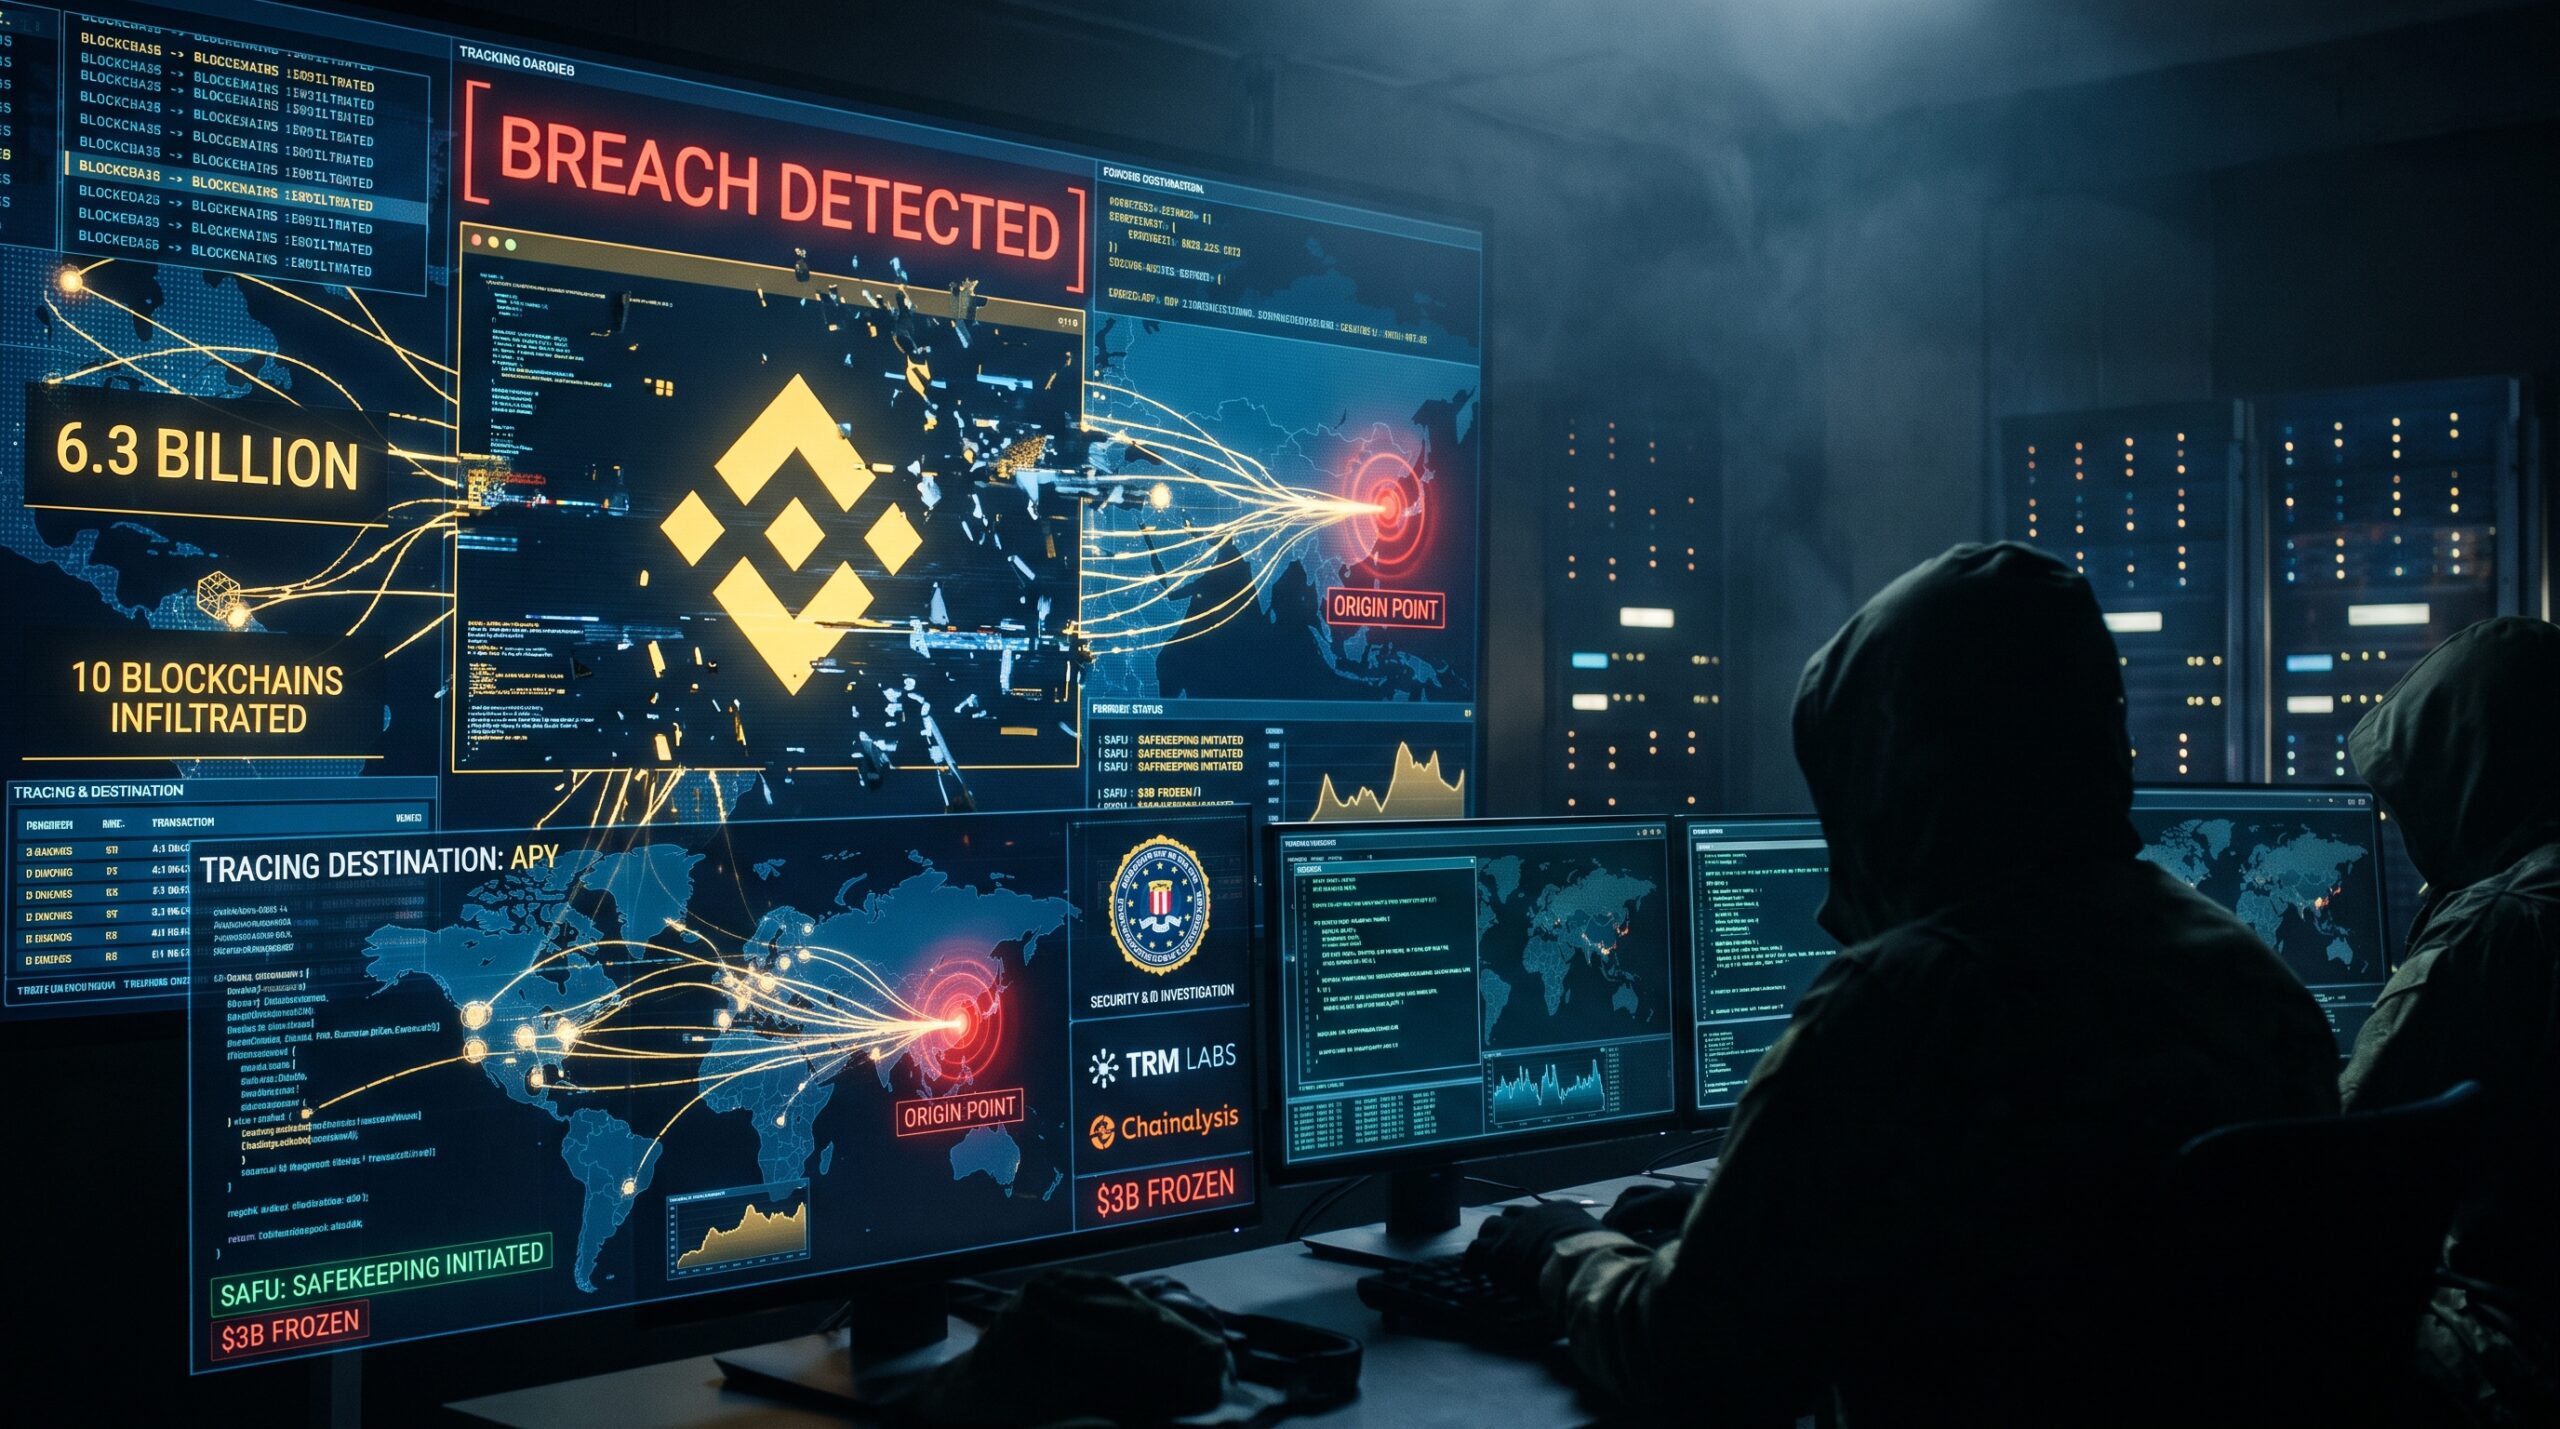
The digital asset sector is reeling from what has been officially logged as the largest cyber heist in history: a lightning-fast breach that drained approximately $6.3 billion from Binance, the world’s largest cryptocurrency exchange.
Within roughly 20 minutes, hackers siphoned funds across 10 different blockchains, prompting immediate emergency responses from industry leaders, global stablecoin issuers, and blockchain forensics experts. As digital investigators began tracing the stolen capital, a strong consensus formed pointing toward a familiar culprit: North Korea.
1. The Anatomy of a Massive Breach
According to preliminary disclosures from Binance and cybersecurity investigators, the attack bypassed traditional security layers through a coordinated multi-step operation:
- The Entry Vector: Initial evaluations pointed toward a compromised developer/DevOps laptop, which allowed unauthorized access into service containers and signing infrastructure.
- Beyond a One-Click Exploit: Binance leadership noted that subsequent deeper probes revealed multiple “points of breach”, ruling out a basic one-click exploit and indicating a heavily sophisticated operation.
- Rapid Response and Freezes: In a race against time, Binance worked alongside industry partners and stablecoin issuers (such as Tether and Circle) to blacklist and freeze roughly $3 billion of the impacted assets. Executives assured users that customer deposits remain safe, with company reserves and the Secure Asset Fund for Users (SAFU) covering all remaining losses.
2. Why Are Experts and the FBI Pointing to North Korea?
Leading blockchain intelligence firms—including TRM Labs and Chainalysis—along with the FBI, have attributed the heist with high confidence to state-backed actors linked to North Korea, specifically pointing to elite units like TraderTraitor (associated with the broader Lazarus Group network).
Investigators tie the incident to Pyongyang for several critical reasons:
- Tactical Parallels: The velocity, cross-chain execution style, and overall technical blueprint closely mirror previous multi-billion-dollar heists, such as last year’s attack on the Bybit exchange.
- State-Sponsored Cyberwarfare: Intelligence agencies and the United Nations have long documented North Korea’s reliance on advanced cryptocurrency theft. With heavy international sanctions crippling its formal economy, state-directed cybercrime has transformed into a vital revenue stream for funding the regime’s military and weapons programs.
3. The Ongoing Battle Over the Remaining Funds
While freezing stablecoins has successfully locked up a major portion of the loot, roughly $2.4 billion in decentralized assets like Bitcoin and Ethereum remain under the attacker’s immediate control. Because these base-layer assets cannot be frozen by any single corporate issuer, analysts warn that the hackers will likely attempt to funnel them through cross-chain mixers and decentralized liquidity pools to launder the funds.
The historic scale of the Binance breach has triggered renewed alarms across the financial world, underscoring just how vulnerable centralized platforms remain to sophisticated, state-sponsored cyber operations.
Leave a Reply