
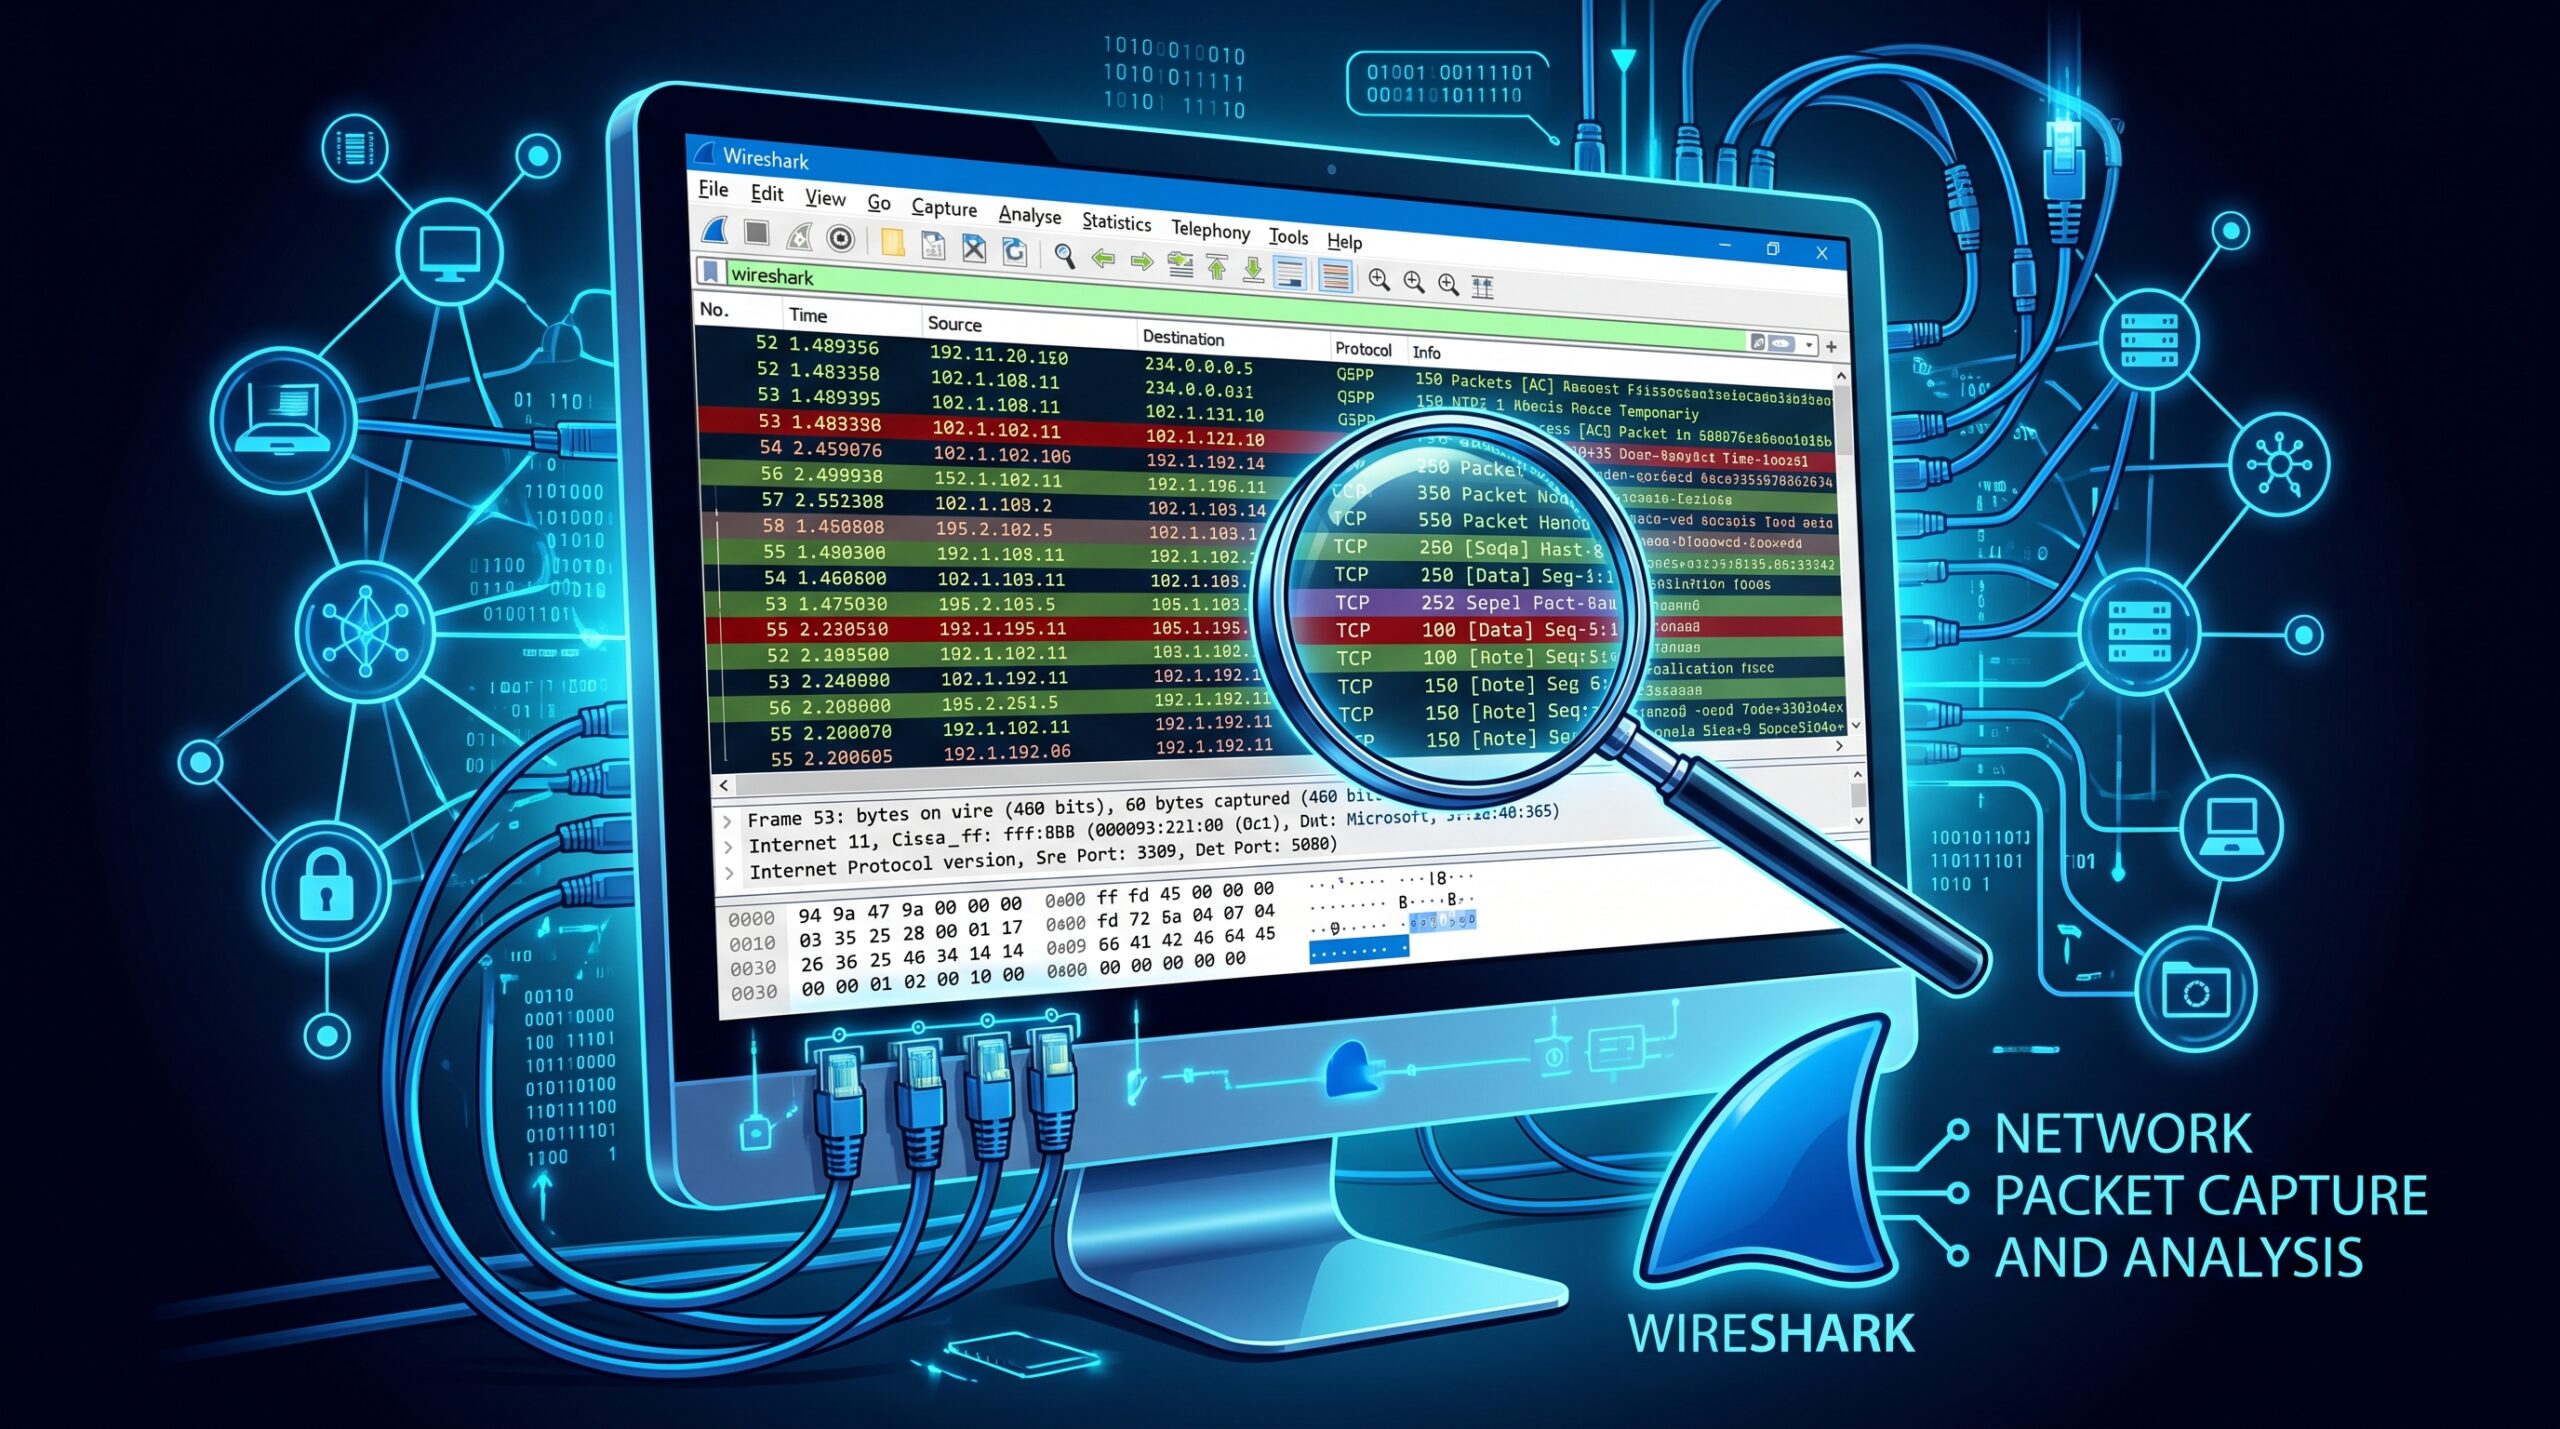
Wireshark is the world’s premier software used to monitor and analyze data (packets) traveling across a computer network in real-time. As a beginner, follow these practical steps to inspect your computer’s data traffic.
1. Download and Install Go to wireshark.org and download the version for your operating system (Windows, macOS, Linux). During installation on Windows, ensure you approve the installation of Npcap, as it is essential for capturing network traffic from your network card.
2. Select a Network Interface Open Wireshark. The main screen displays a list of all available network interfaces (e.g., Wi-Fi, Ethernet). Look for the interface with an actively moving sparkline graph next to it (usually your active Wi-Fi connection) and select it.
3. Start Packet Capture Double-click your selected interface or click the blue shark fin icon in the top left corner. You will immediately see lines of data (packets) scrolling rapidly down the screen, representing all traffic flowing in and out of your machine.
4. Use Display Filters To isolate specific traffic from the thousands of captured packets, type the following into the top filter bar and press Enter:
- http: Filters for unencrypted web traffic.
- dns: Shows domain name queries.
- tcp.port == 443: Filters for secure HTTPS traffic.
- ip.addr == 192.168.1.5: Isolates traffic to or from a specific IP (replace the numbers with your target IP).
5. Inspect a Packet Click on any packet row in the main list. In the middle pane (Packet Details), expand the layers of the OSI model to inspect the sender’s MAC address, IP address, port numbers, and application protocol details.
6. Stop and Save Click the red square icon in the top left corner to stop capturing data. Go to File > Save to export the capture as a .pcapng file for later analysis.
Security Note: Wireshark can reveal passwords and usernames in plain text on unencrypted protocols (like HTTP or FTP). Only use it on networks you own or have explicit authorization to monitor.
Leave a Reply